
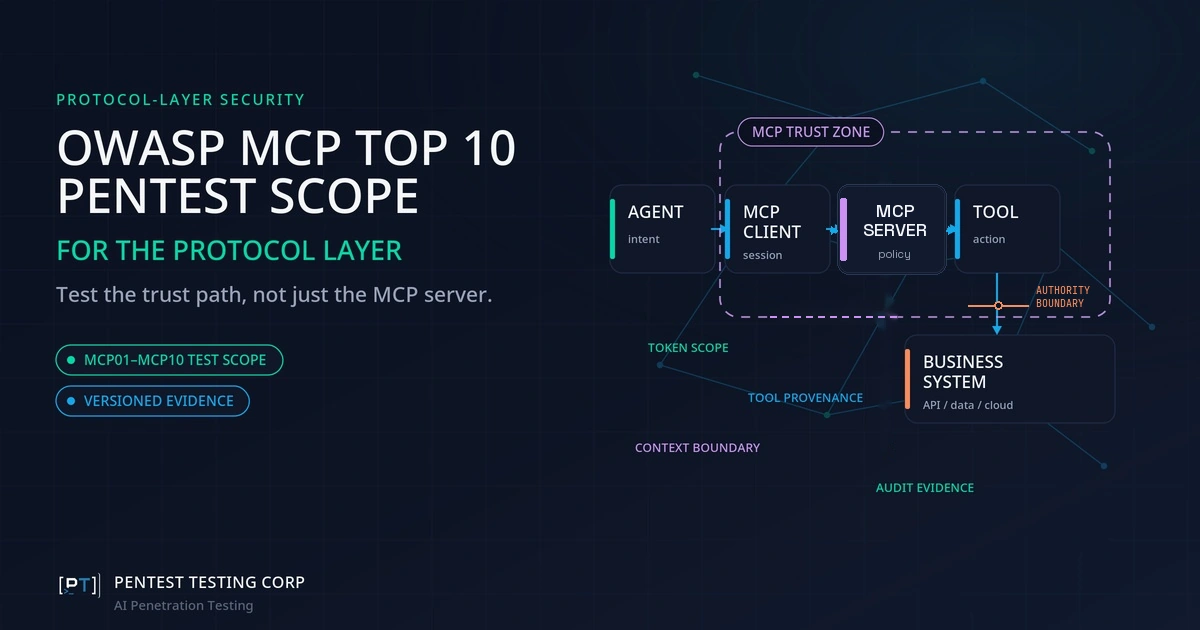
OWASP MCP Top 10 Testing
OWASP MCP Top 10 Testing: A Pentest Scope for the Protocol Layer A CISO receives an enterprise security questionnaire with
OWASP MCP Top 10 Testing: A Pentest Scope for the Protocol Layer A CISO receives an enterprise security questionnaire with
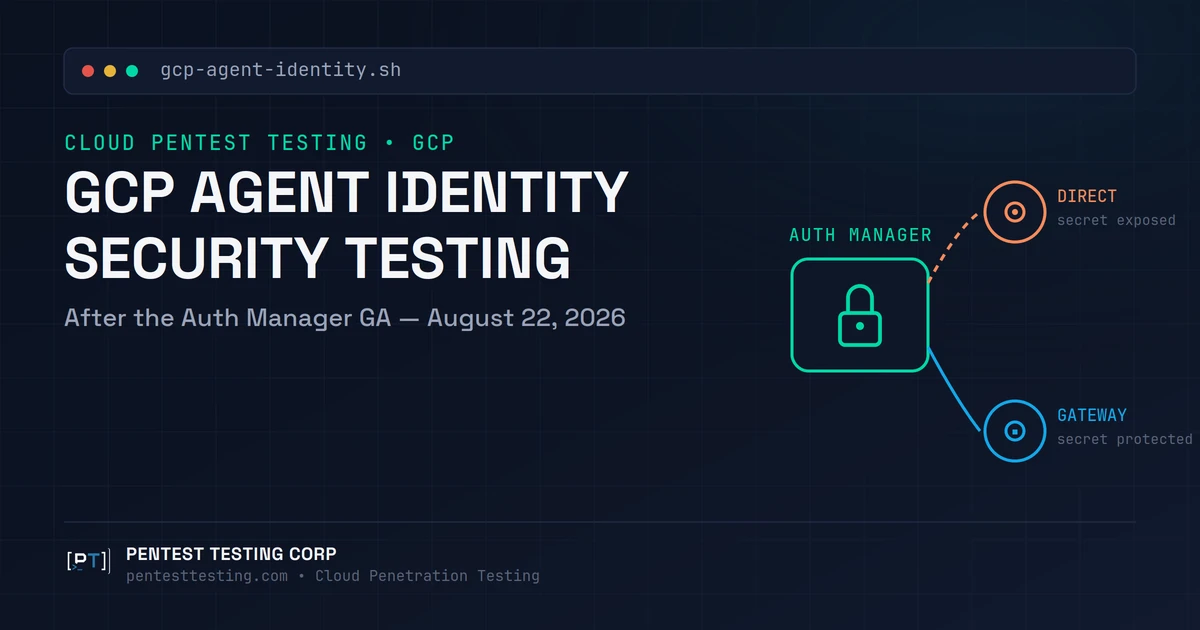
GCP Agent Identity Security Testing After the Auth Manager GA A platform engineering team at a mid-market SaaS company spent
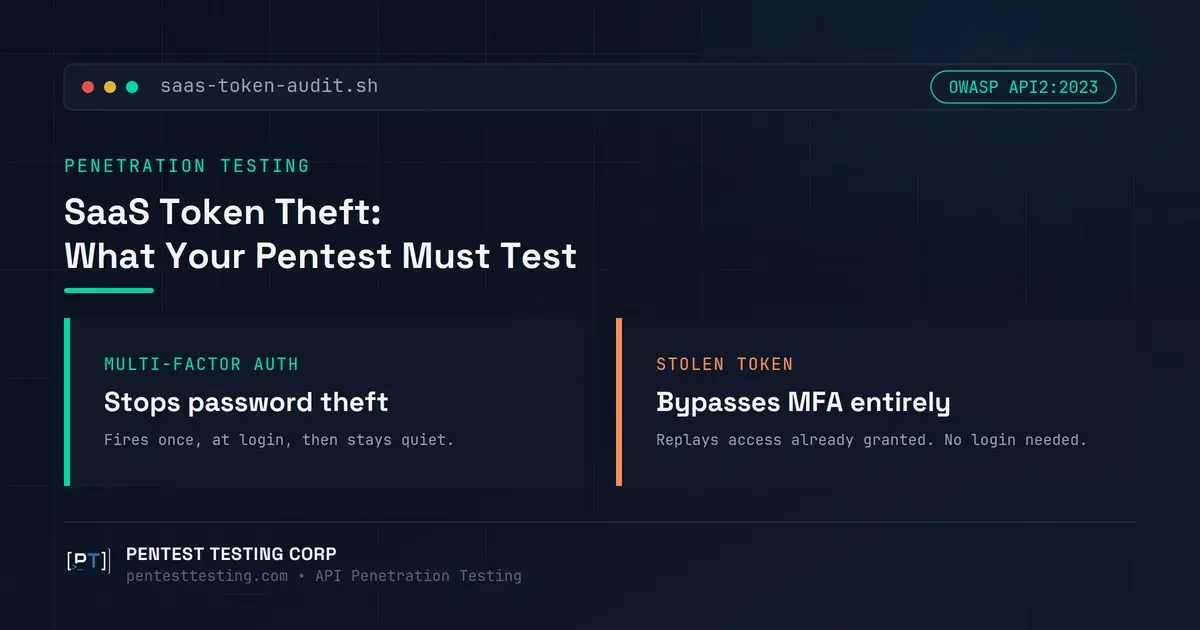
SaaS Token Theft Penetration Testing: What Your Next Pentest Must Cover A SaaS security team preparing for an enterprise renewal
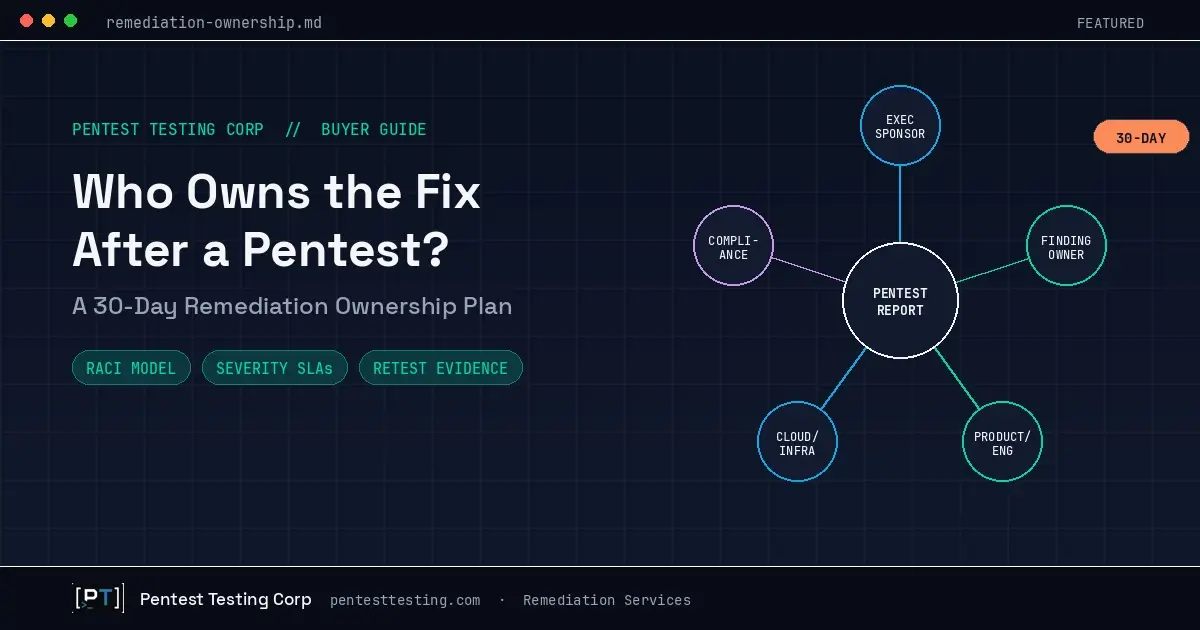
Who Owns the Fix After a Pentest? A 30-Day Remediation Ownership Plan A pentest report lands in a shared inbox
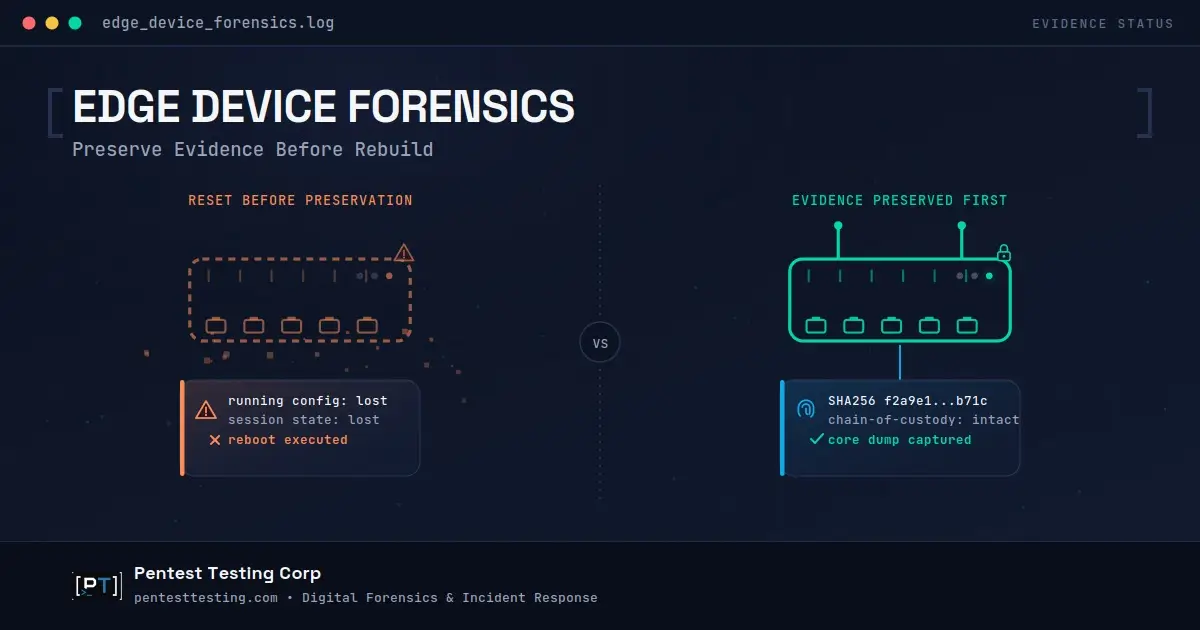
Edge Device Forensics: Preserve Evidence Before Rebuild A regional insurer’s network team gets an alert: their SD-WAN manager pushed a
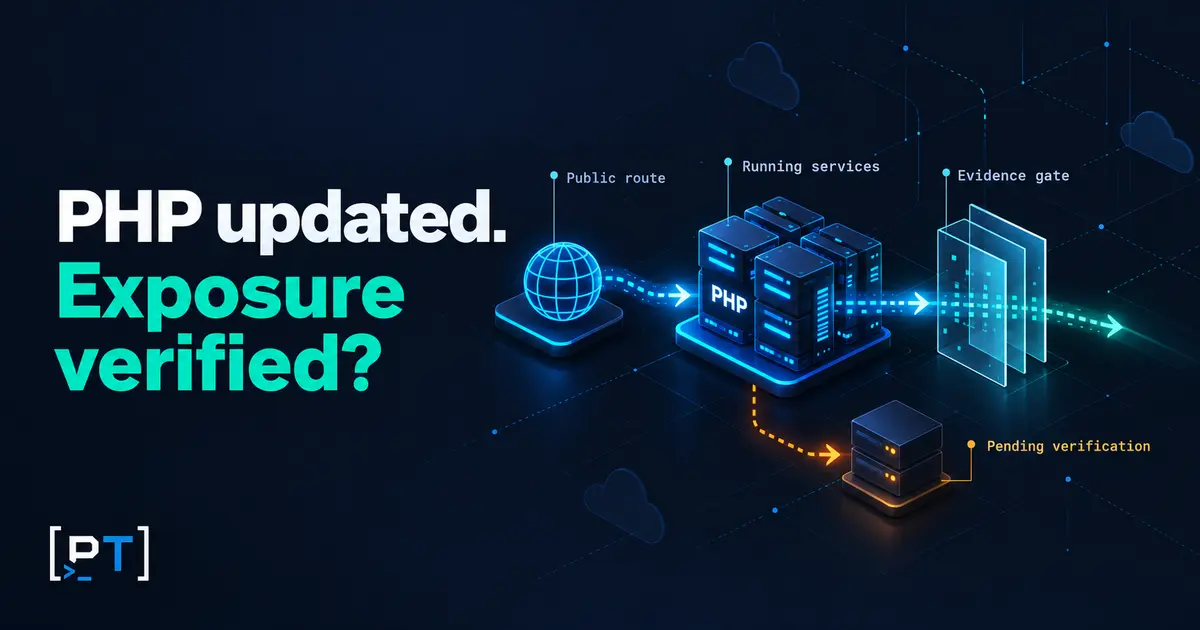
Post-Patch External Penetration Testing: Validate PHP Exposure Is Closed A PHP security update has been deployed; the emergency change is
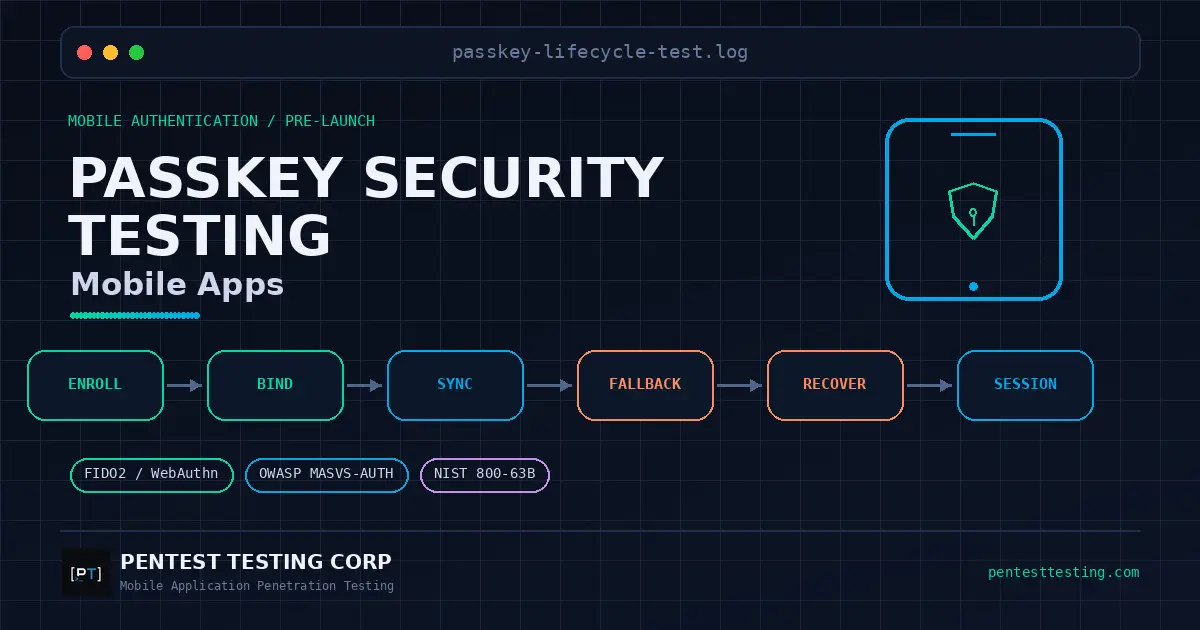
Passkey Security Testing for Mobile Apps A mobile product team is preparing a passkey-first login for its next iOS and
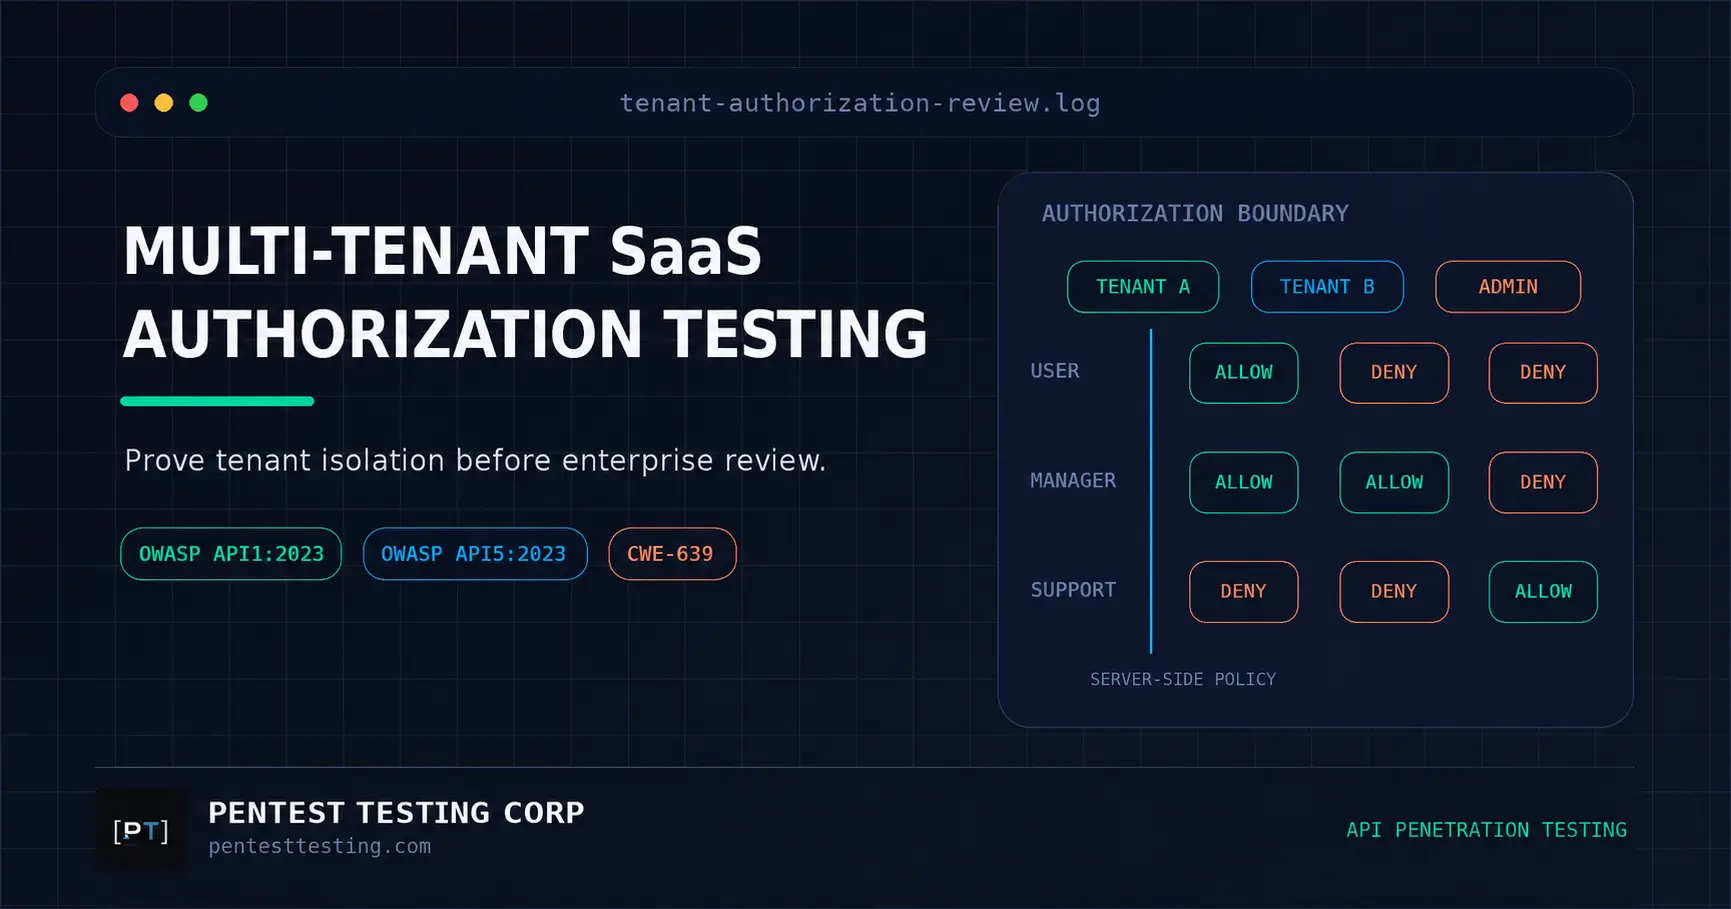
Multi-Tenant SaaS Authorization Testing Before Enterprise Review An enterprise prospect is ready to sign. Procurement has your SOC 2 report,
Multi-Tenant SaaS Authorization Testing Before Enterprise Review Read Post »
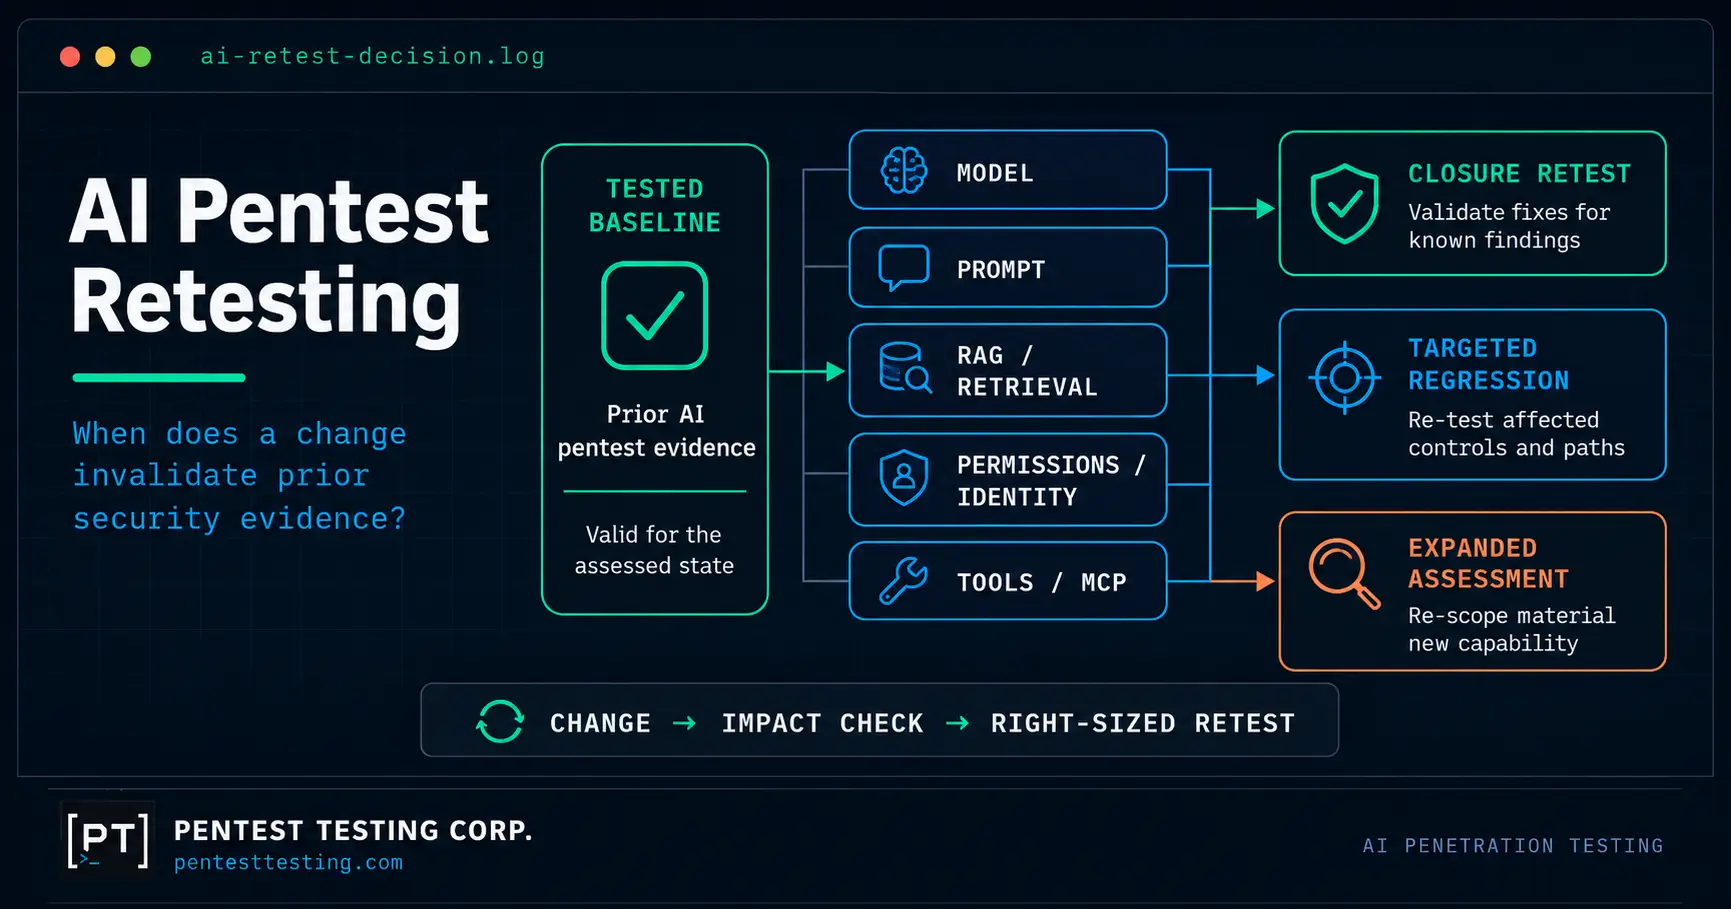
AI Pentest Retesting After Model and Tool Changes A product team closes the last high-risk finding from an AI penetration
AI Pentest Retesting After Model and Tool Changes Read Post »
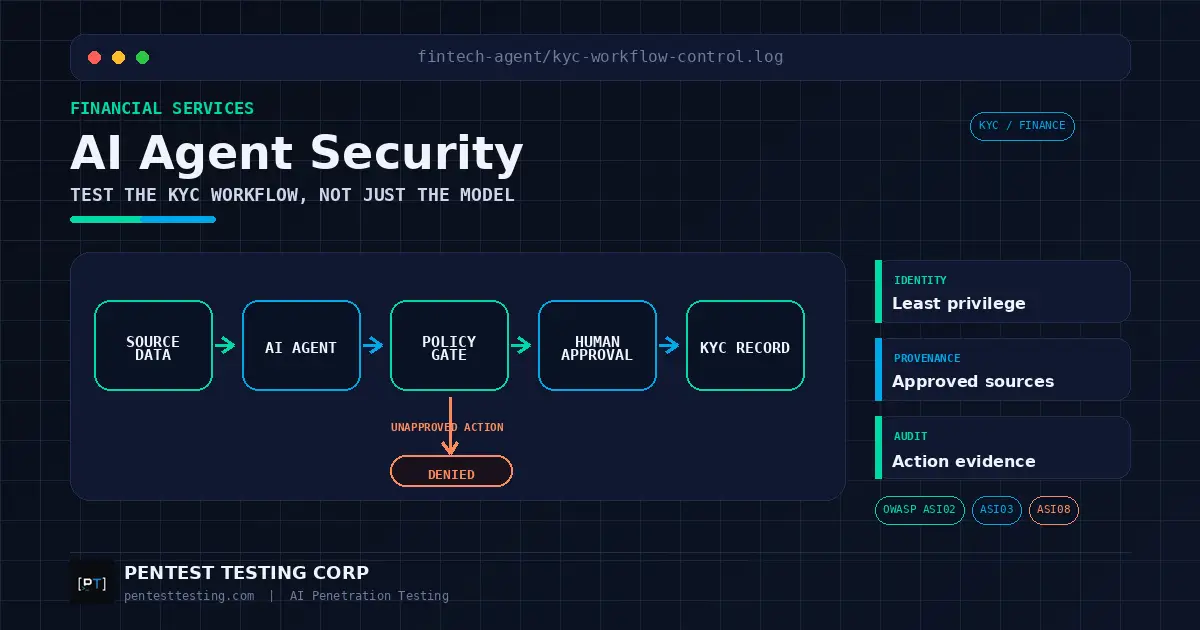
Financial Services AI Agent Security: Test KYC Workflows A fintech team is preparing to move a KYC agent from pilot
Financial Services AI Agent Security for KYC Workflows Read Post »