
ISO 27001 Penetration Testing Audit Evidence Guide
ISO 27001 Audit Readiness: How Penetration Testing Proves Your Controls Actually Work ISO 27001 is not just about having policies, […]
ISO 27001 Penetration Testing Audit Evidence Guide Read Post »
ISO 27001 Audit Readiness: How Penetration Testing Proves Your Controls Actually Work ISO 27001 is not just about having policies, […]
ISO 27001 Penetration Testing Audit Evidence Guide Read Post »
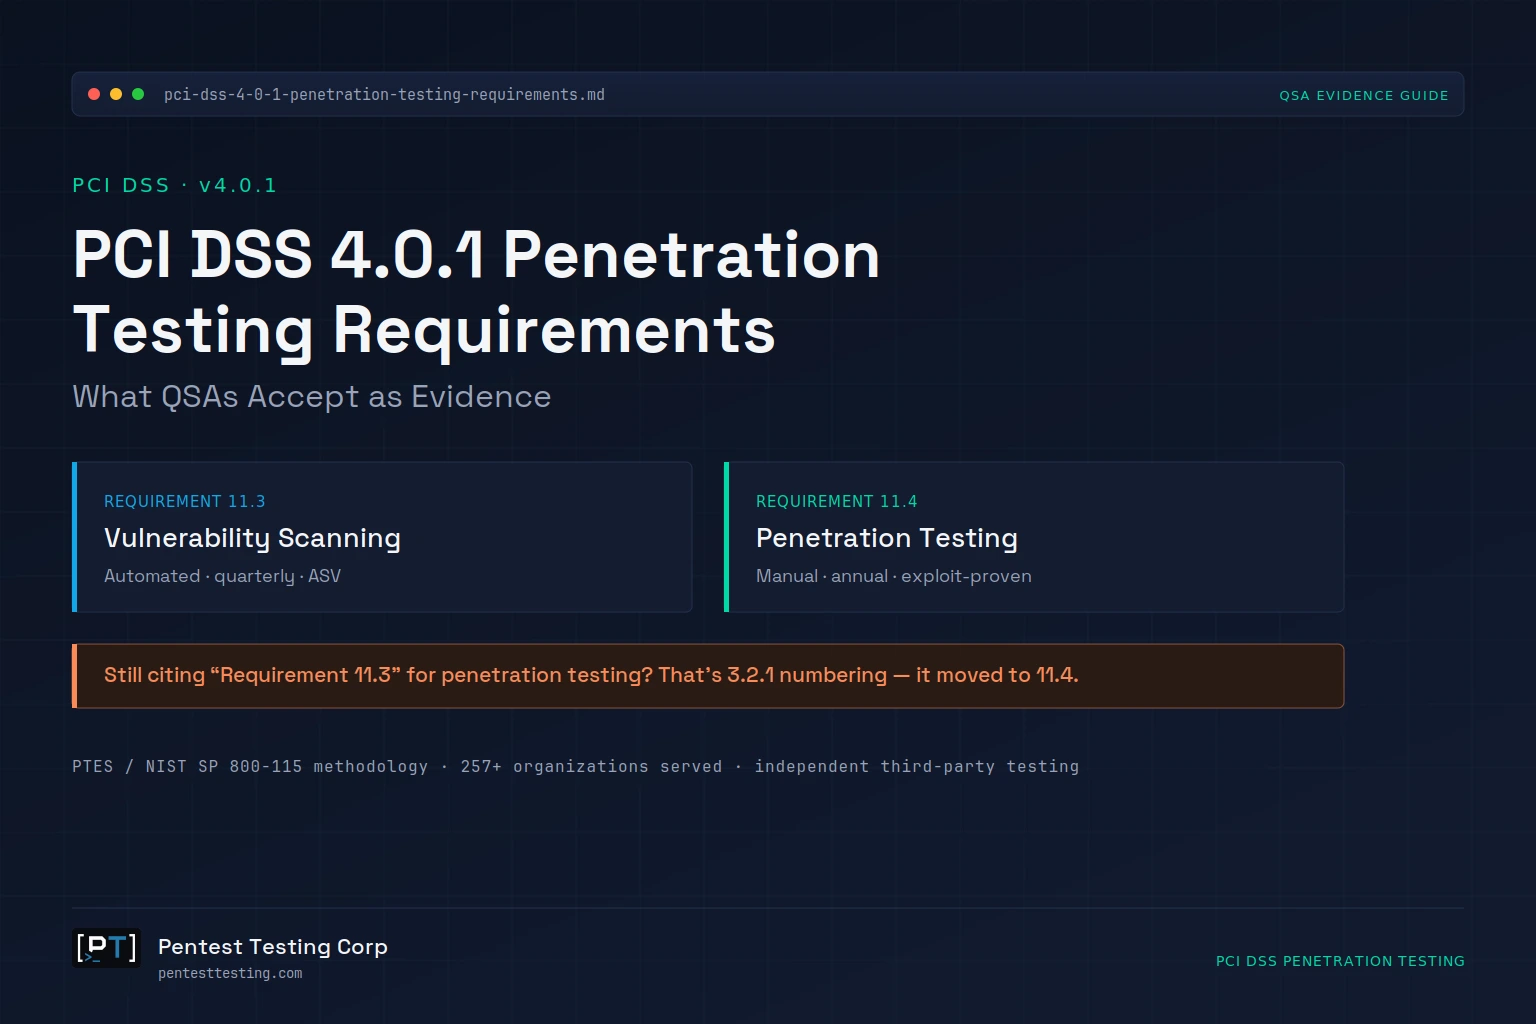
PCI DSS 4.0.1 Penetration Testing Requirements: What Counts as QSA-Ready Evidence Most organizations preparing for a QSA review already know
SOC 2 Audit Failing? Why Your Penetration Test Isn’t Enough (and What Auditors Actually Expect) You Did a Pentest… So
SOC 2 Penetration Testing Requirements 2026: Why Audits Fail Read Post »
7 Critical Vulnerabilities We Found in SaaS Applications (Real Case Studies) SaaS buyers do not lose deals because a product
What to Expect in a Professional Penetration Testing Report (With Sample) When a buyer asks for a penetration testing report
Best Time to Perform a Penetration Test Before Product Launch Launching a SaaS product without proper security testing isn’t just
API Penetration Testing Checklist for PCI DSS Compliance If your APIs touch payment data, you’re already exposed. Not hypothetically. Right
Web Application Penetration Testing Cost in 2026 (Detailed Breakdown) Introduction: The real cost isn’t the pentest. It’s the breach you
How to Choose a Penetration Testing Company for SOC 2 Compliance When a deal stalls because a prospect asks, “Are
Collaboration Platform Phishing Investigation: Business Email Compromise Without Email Business email compromise no longer lives only in the inbox. Attackers
Collaboration Platform Phishing Investigation for BEC Read Post »