
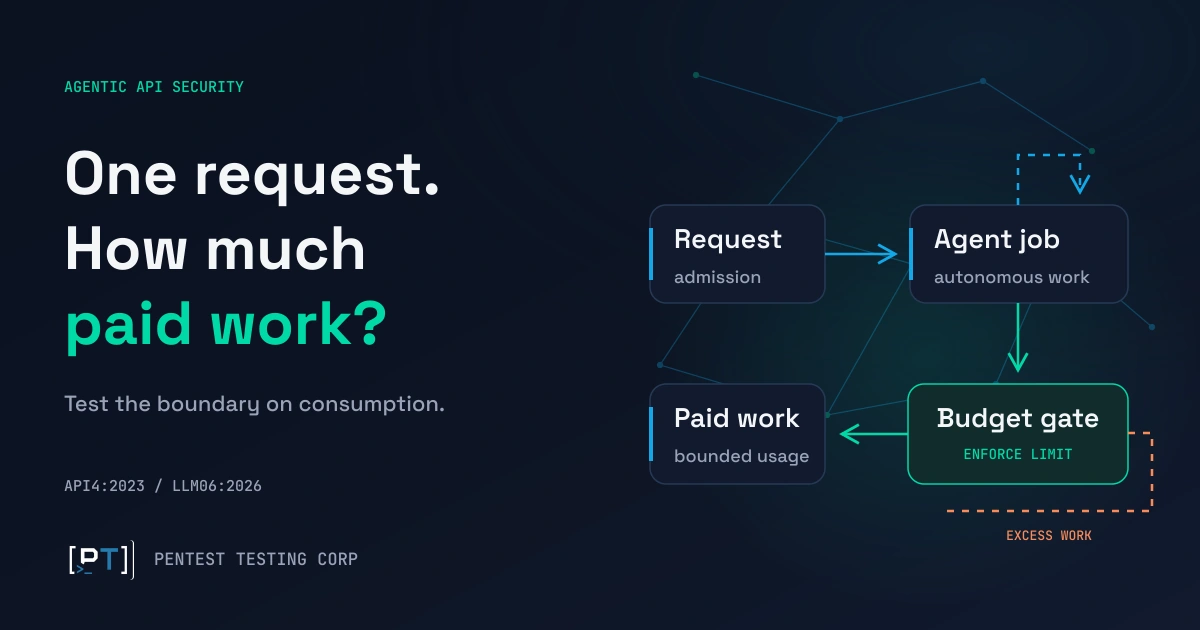
AI Agent API Abuse Penetration Testing
AI Agent API Abuse Penetration Testing: Rate Limits and Cost Controls A CTO is preparing to launch an agent that
AI Agent API Abuse Penetration Testing: Rate Limits and Cost Controls A CTO is preparing to launch an agent that
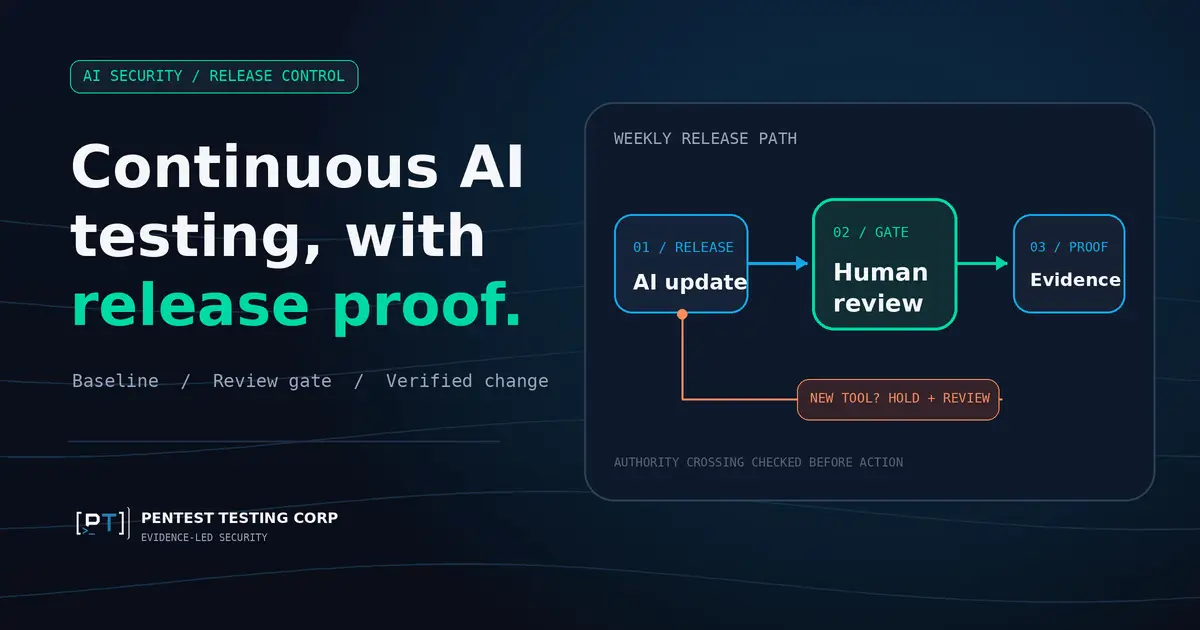
Continuous AI Penetration Testing PTaaS: Scope It Around Releases Your engineering team releases an AI assistant update every Thursday. One
Third-Party AI Agent Incident Response: A DFIR Playbook Your incident commander receives a vendor notice at 09:15: an AI agent
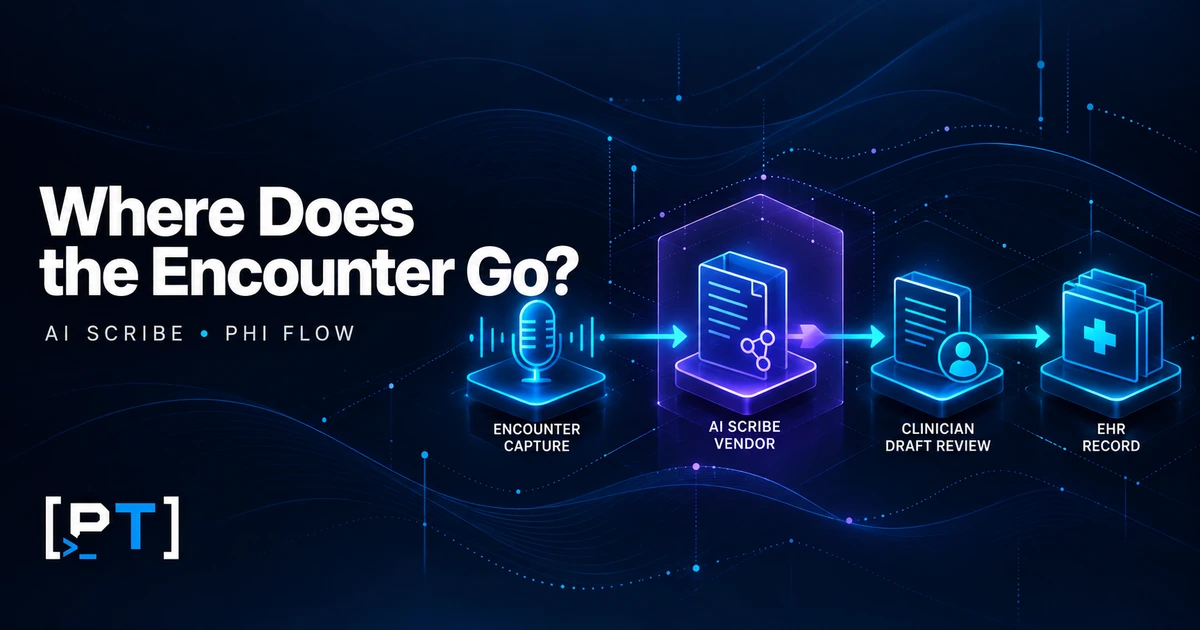
HIPAA AI Medical Scribe Security Testing: What a Healthcare Pentest Must Cover A practice group is ready to roll out
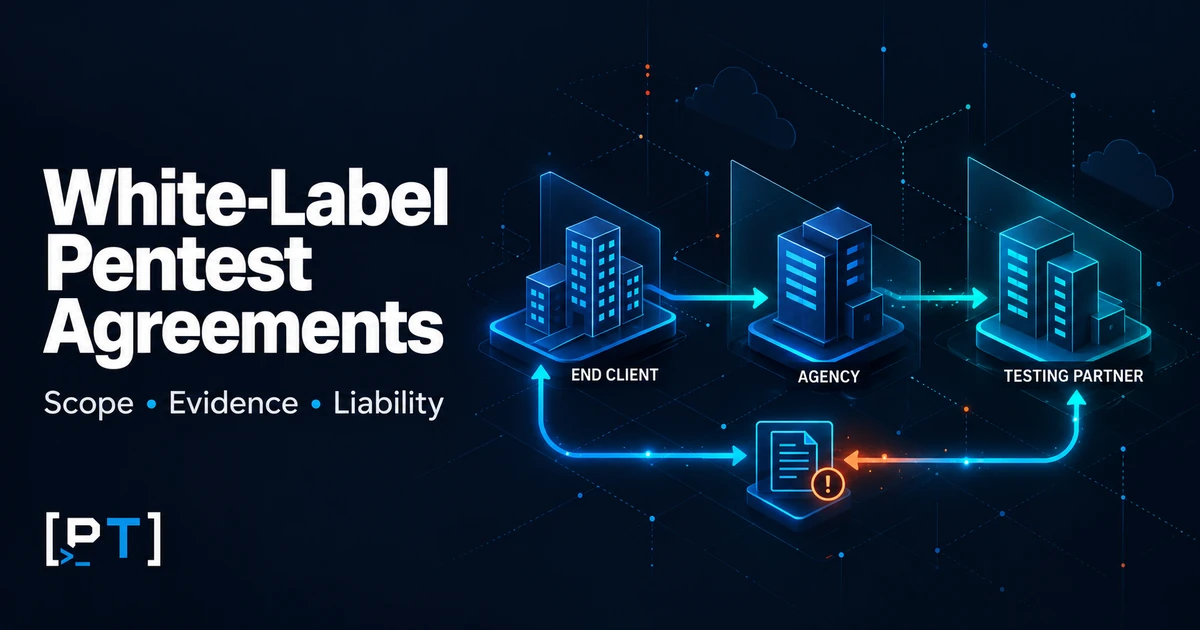
White-Label Penetration Testing Agreement: Scope, Evidence, and Liability An agency wins a new SaaS client, and the client’s enterprise prospect
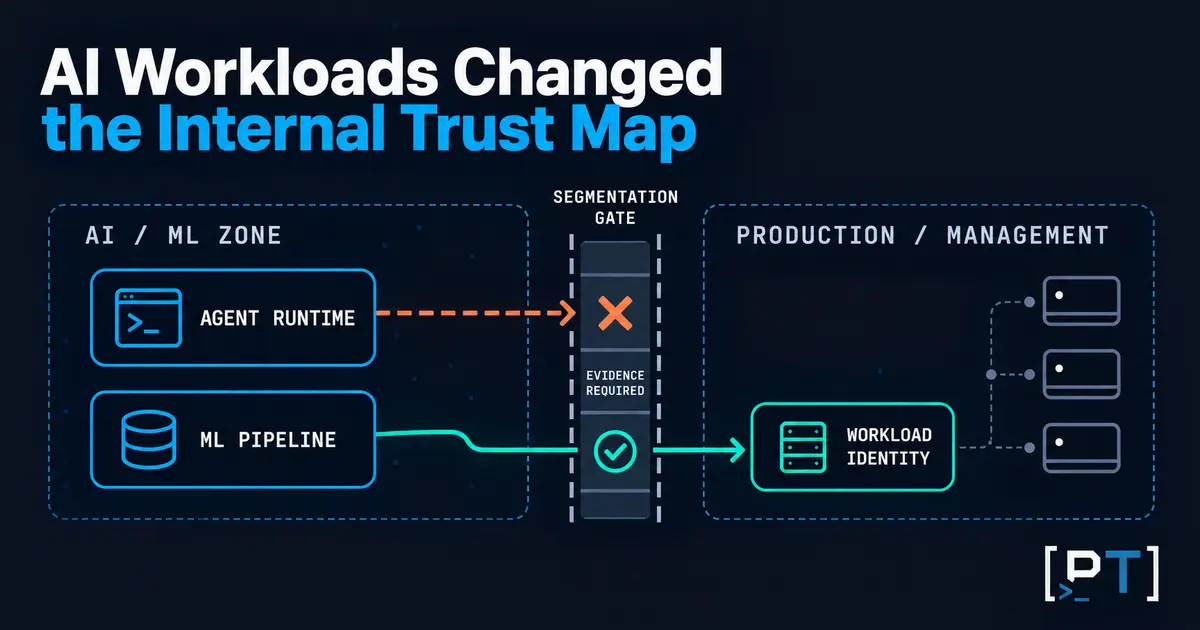
Internal Network Segmentation Testing for AI Workloads Internal network segmentation testing becomes a leadership priority when AI workloads begin connecting
Internal Network Segmentation Testing for AI Workloads Read Post »
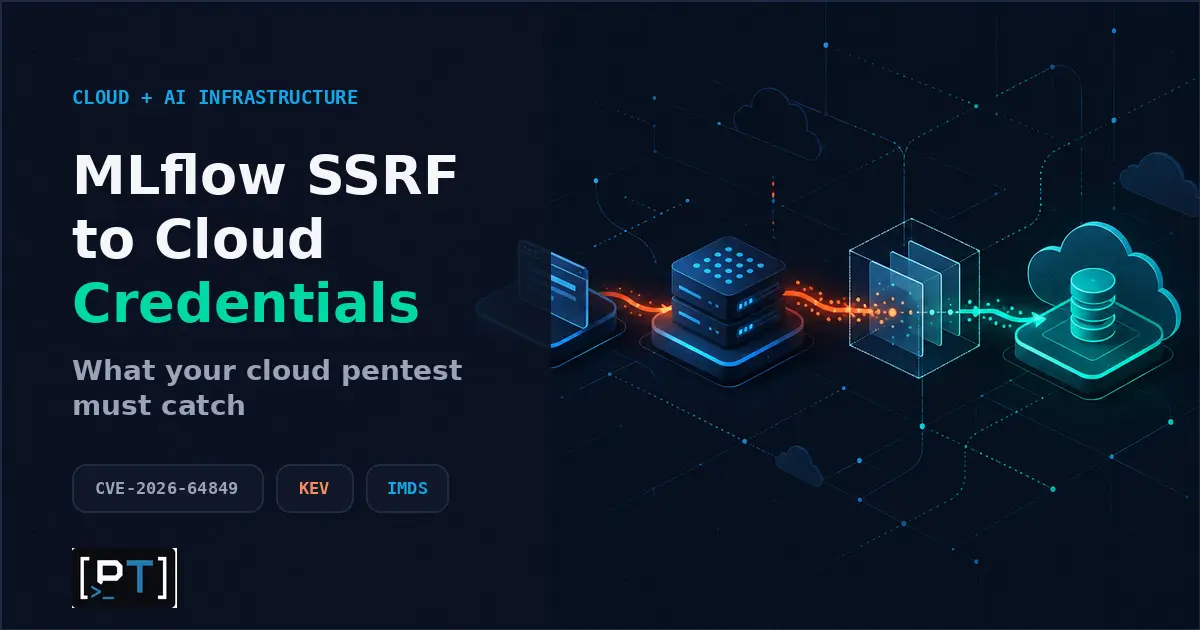
MLflow SSRF to Cloud Credentials: What Your Cloud Pentest Must Catch Your ML platform owner confirms that MLflow has been
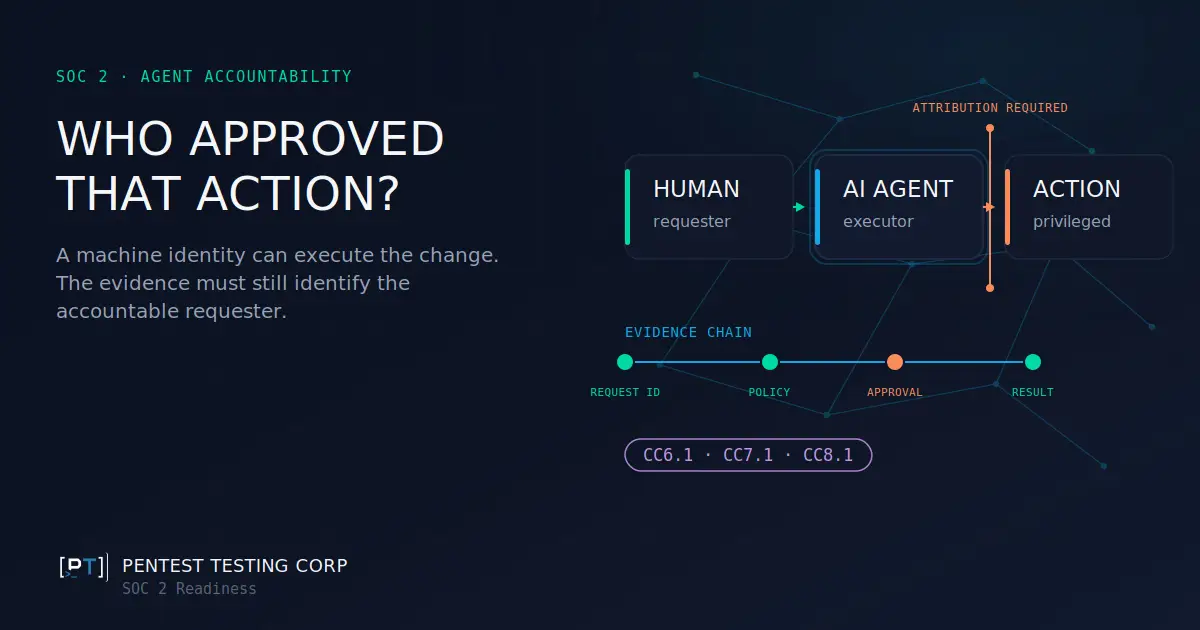
Who Approved That? AI Agent Accountability for SOC 2 A finance agent updates a customer’s payment terms at 2:14 a.m.
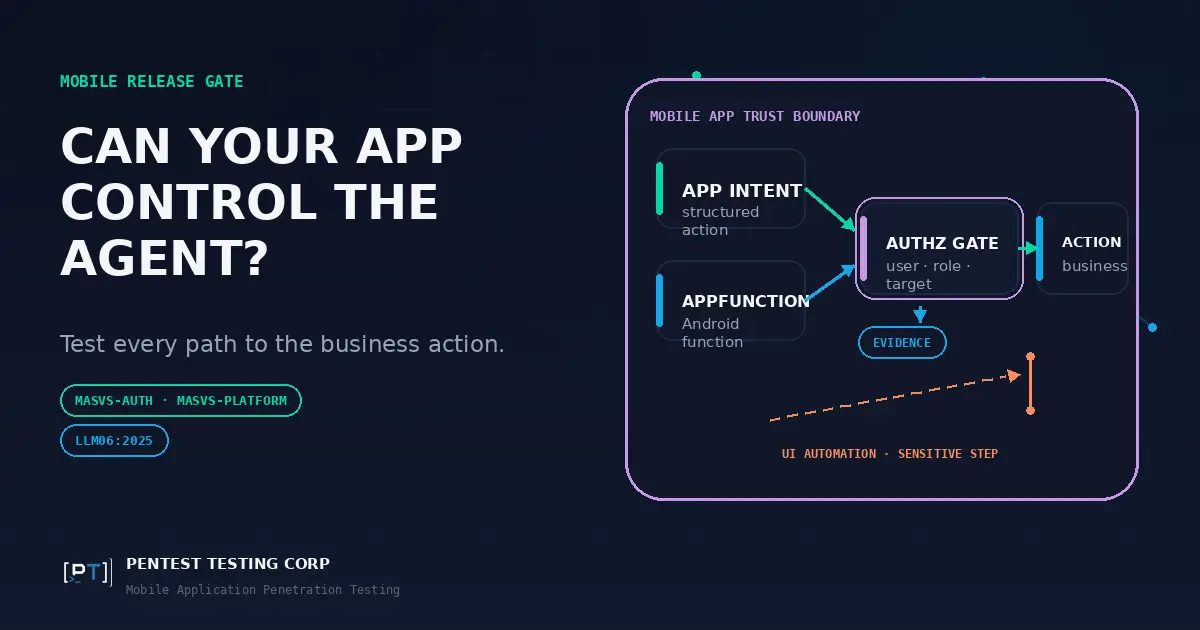
Agent-Actionable Mobile App Security Testing A mobile product team is preparing its next iOS and Android release. Functional QA confirms
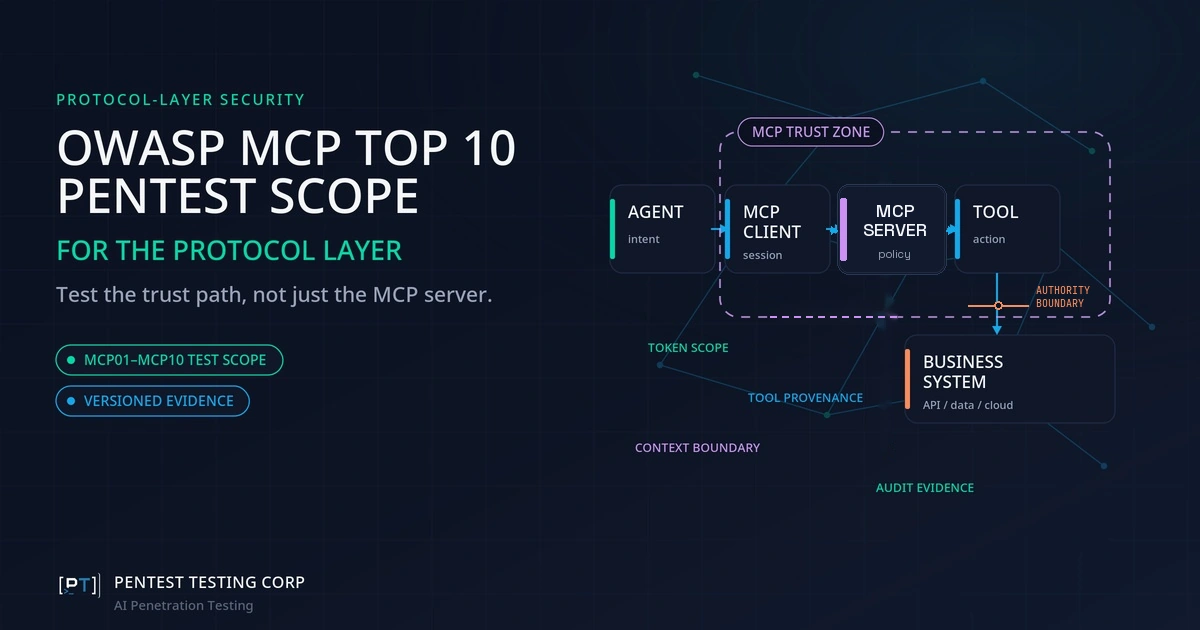
OWASP MCP Top 10 Testing: A Pentest Scope for the Protocol Layer A CISO receives an enterprise security questionnaire with